A hospital decommissioning project usually starts with a storage room full of equipment nobody has looked at in a while: retired workstations from a nursing unit, laptops from a clinic that merged last spring, drives pulled from an imaging archive, and a multifunction printer nobody remembers leasing. Any of those devices may still hold patient data, and once they leave the building, your organization is still accountable for it.
Getting that equipment out the door safely is the job of an IT asset disposition (ITAD) vendor. Hospital IT teams vet EHR partners carefully because those partners handle patient data. An ITAD vendor handles the same data at the end of its life, and it deserves the same level of scrutiny.
Why the Stakes Are Higher in Healthcare
Healthcare has been the costliest industry for data breaches for 13 consecutive years, with IBM’s 2026 Cost of a Data Breach Report putting the average at $6.64 million per incident.
The HIPAA Security Rule is clear: covered entities need written policies and procedures for the final disposition of ePHI and the hardware or media storing it, plus procedures for removing ePHI before that media is reused. How you get there, whether by clearing, purging, or physically destroying the media, depends on the circumstances. Because HIPAA doesn’t dictate a single method, the decision about how each device gets sanitized often falls to your ITAD vendor, and their methods become part of your compliance record.
The Checklist
1. Certifications You Can Verify Yourself
Ask for current certificates, then confirm them. NAID AAA certification comes from i-SIGMA, the standards-setting body for the information destruction industry. Certified providers go through both scheduled and unannounced audits to maintain NAID AAA status, so a certified vendor has to follow its documented process every day, not only when an auditor is expected. R2v3 covers responsible reuse, repair, and recycling. ISO 9001, 14001, and 45001 speak to quality management, environmental controls, and worker safety.
2. A Signed Business Associate Agreement Before Pickup
HIPAA generally requires covered entities to contract with business associates so those associates will appropriately safeguard protected health information, and the same requirement extends to their subcontractors. Have your ITAD vendor sign a business associate agreement (BAA) before they pick up any equipment. Read the breach notification and subcontractor terms closely. If your vendor sends any drives to another company for shredding or recycling, ask for that company’s name and confirm it’s covered by the BAA.
3. Sanitization Methods Tied to Current NIST Guidance
In September 2025, the National Institute of Standards and Technology (NIST), the federal agency behind the most widely referenced data sanitization standard, released Revision 2 of its media sanitization guidelines. The update puts more weight on documented, organization-wide sanitization programs.
For a hospital, that means your ITAD vendor’s process becomes part of your own program, so it’s worth knowing how it works. Ask which version of NIST’s guidelines they follow, how they handle SSDs and encrypted drives, which store data differently than traditional hard drives, and how they confirm and document that each wipe actually worked.
4. Chain of Custody You Can See in Real Time
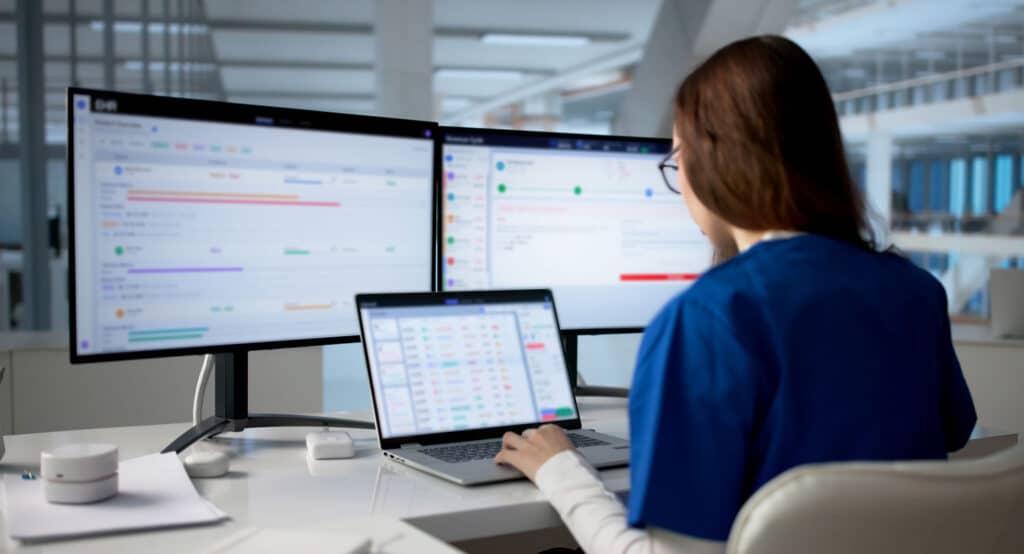
Your vendor should track every device by serial number from the moment it leaves your loading dock until it’s wiped, shredded, or resold. Equipment should travel in secured vehicles, and your team should be able to check the status of any asset through an online portal instead of emailing the vendor and waiting days for an answer. When destruction is complete, you should receive certificates of destruction promptly, with each one listing the serial numbers of the devices destroyed.
5. On-Site Shredding and Witness Options
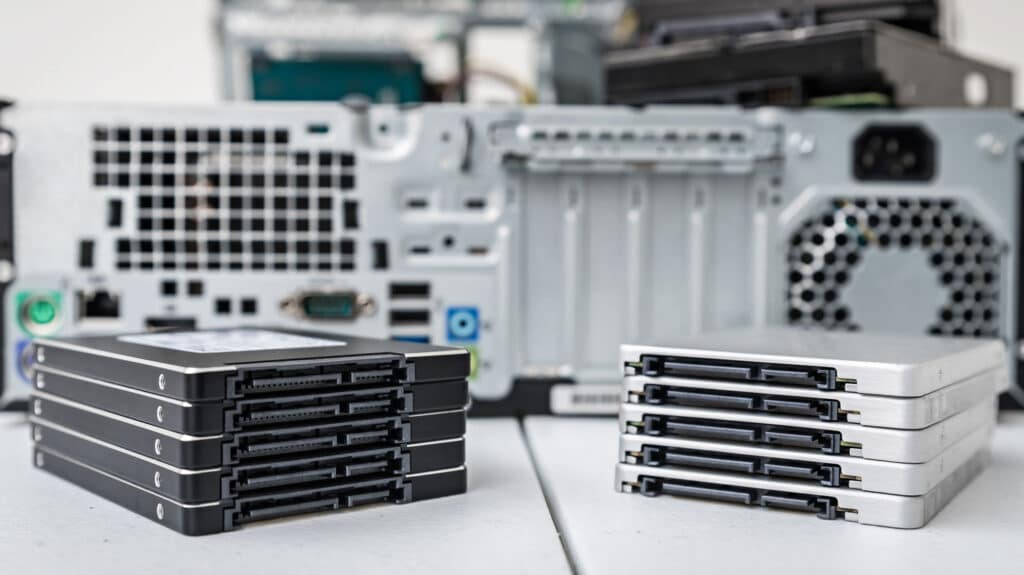
Some hospitals choose to destroy certain drives on-site so the data never leaves the building. Drives holding especially sensitive records, like those from behavioral health or research departments, are common candidates. If that’s part of your policy, look for a vendor that offers mobile shredding, where a truck-mounted shredder destroys drives at your facility, and lets your staff watch the process and sign off when it’s complete.
6. Insurance and Cyber Coverage That Matches Your Risk
Ask each vendor for proof of insurance, including cyber liability coverage, and check that the limits match the size of your organization. Coverage at the levels a health system needs is expensive and hard to qualify for, so vendors without it often stand out quickly. If a vendor’s coverage is too low, your organization may be left covering the cost of a breach that happens on their watch.
7. Capacity to Scale Across a Health System
Retiring equipment for a single community hospital is a very different job than doing it across a 20-facility health system. Before signing, make sure your vendor can handle the volume, the number of locations, and reporting you require.
Your vendor should coordinate pickups across states, support data center decommissioning for on-premises infrastructure, and keep reporting consistent no matter which site the assets came from.
8. Transparent Value Recovery
Old equipment often still has resale value, and the money it brings in can help cover the cost of your disposal project. Ask each vendor how they test and grade equipment for resale, who they sell it to, and how they report the revenue back to you. A vendor that provides a monthly reconciliation, a statement showing what was sold and what you earned, gives your team clear numbers to review and to present when budgets are discussed.
How TAMS Measures Up
For more than two decades, TAMS has helped large and enterprise organizations retire IT assets without putting their data at risk.
Our certifications are public, and you can view each one: NAID AAA, R2v3, ISO 9001:2015, ISO 14001:2015, and ISO 45001:2018. Our data destruction services are also audited every year by qualified PCI QSA/ISA auditors.
Clients get access via portal to real-time inventory, certificates of destruction, and monthly financial reconciliations. We handle data erasure and hard drive shredding, including mobile shredding, with witness options available. Our data center and pickup teams work nationwide. And because our processing is thorough, many buyers pay more for equipment that has come through our facility, so more of that value returns to your budget.
Talk Through Your Next Decommission With Us
Replacing workstations across your nursing units, retiring servers after an EHR migration, or absorbing equipment from a newly acquired clinic? Reach out to the TAMS team and walk us through it. We’ll show you how we move assets from your floor to final disposition.